Practice Protect (Idira Identity) provides several predefined roles to help manage user access and administrative permissions. Two commonly used predefined roles are Everybody and System Administrator.
By default, members of the System Administrator role have full administrative rights and can perform all administrative tasks. If you want to delegate full administrative access to additional users, you can add them to the predefined System Administrator role.
If you only want to delegate specific administrative responsibilities, you can create custom roles with the required administrative rights before assigning users to those roles. This allows you to control which administrative tasks users can perform without granting them full administrative access.
Prerequisites
- An account with admin rights in Practice Protect.
-
Ensure the users are already members of the role to which you want to assign administrative rights.
Assigning Administrative Rights
-
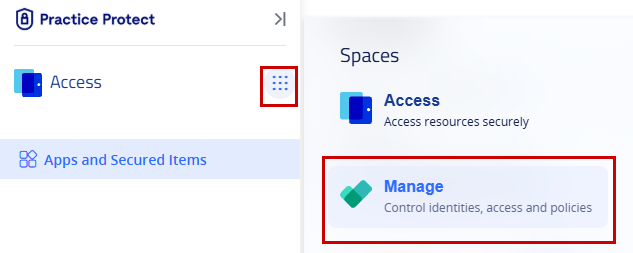
- Log in to Practice Protect and switch to Manage Space.
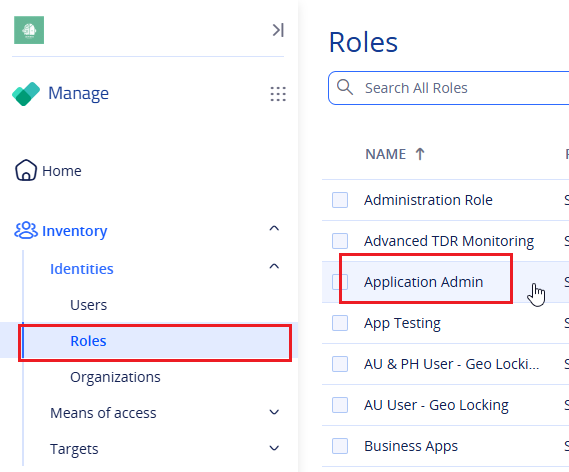
- In the navigation menu, expand Inventory > Identities > Roles to view the available roles.
- Open an existing role to assign administrative rights. If no suitable role exists, create a new role by following the Creating Roles guide.
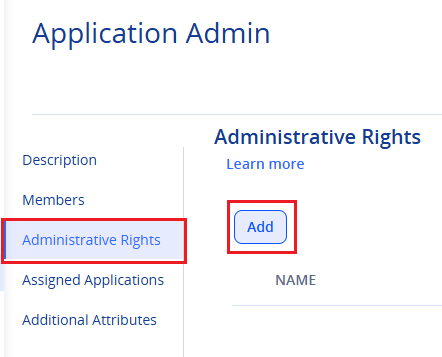
- Go to the Administrative Rights tab and click Add to assign administrative rights to the role.
- Log in to Practice Protect and switch to Manage Space.
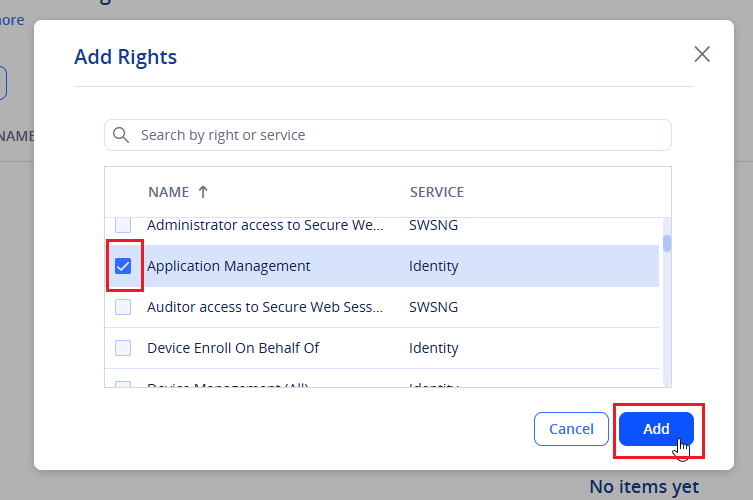
- Select the checkbox next to each administrative right you want to assign to the role, then click Add. In this example, we selected Application Management.
NOTE: For description of each administrative right, see the List of Administrative Rights. - Click Save in the bottom-right corner to apply the changes.
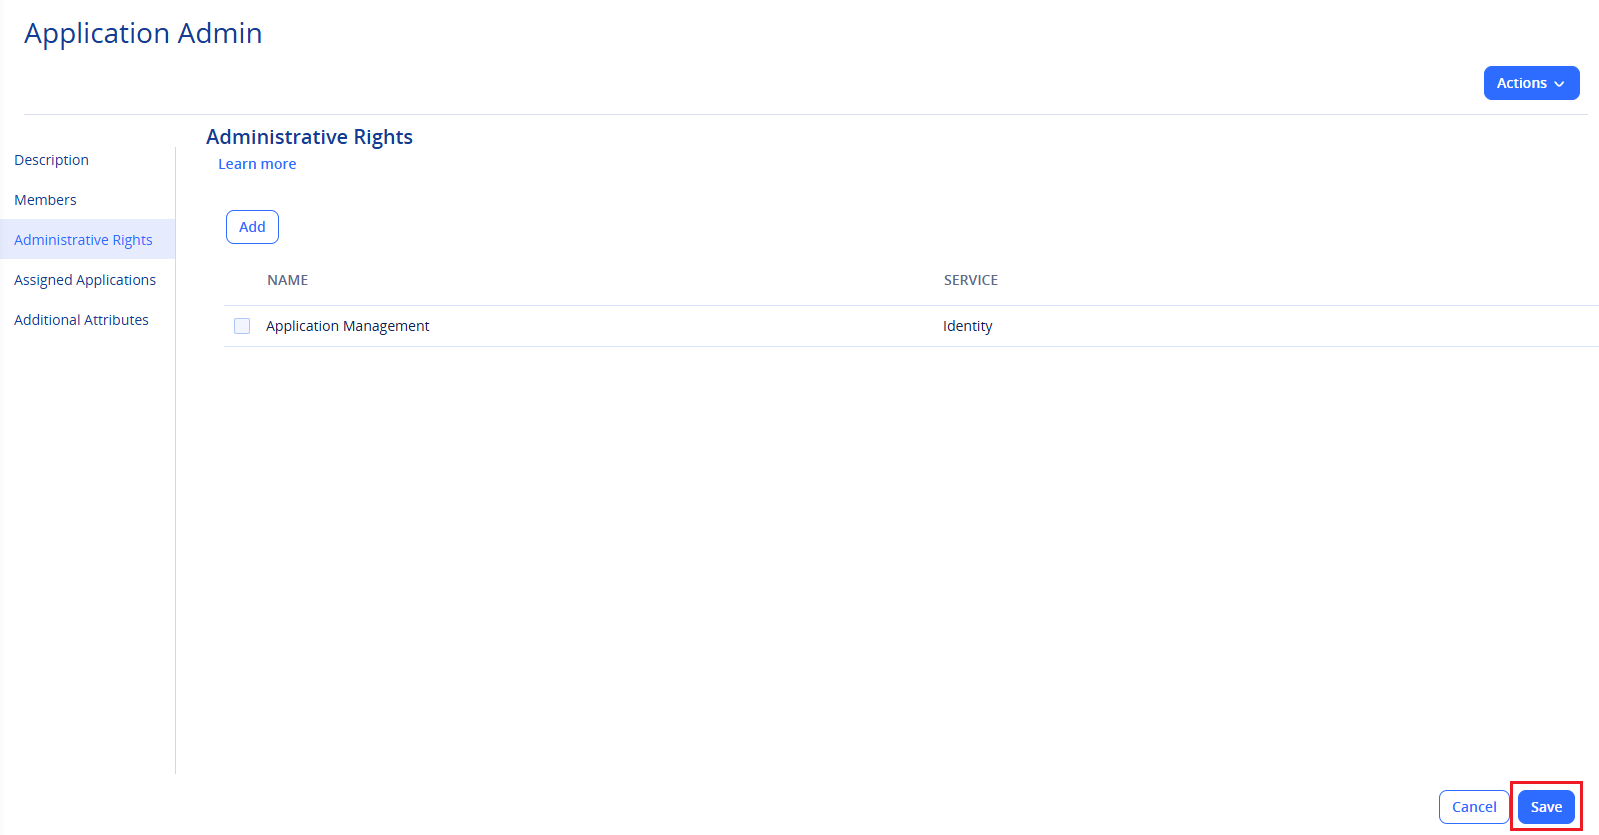
- Users who are members of the role will now have the assigned administrative rights, such as Application Management, based on the permissions configured for the role.